Briefing
SOC 2 risk management: the governance layer behind the controls
SOC 2 risk management is how leadership decides which risks matter and which controls answer them. So it sits above individual controls, and the CPA firm looks for evidence of it.
- Six specialist brands
- CPA firms and QSAs sign the reports
- One place to start
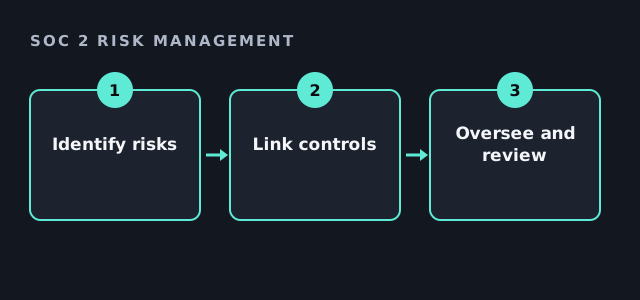
What the criteria expect from SOC 2 risk management
The Trust Services Criteria include risk assessment and monitoring. Therefore an organisation must identify risks to its objectives, assess them and respond.
Fraud risk and significant change are named too. Also, oversight by leadership is part of the control environment.
Building a SOC 2 risk management process
The process does not need to be heavy. However, it must run on a schedule and leave a record.
| Step | Evidence |
|---|---|
| Identify risks | A dated risk register |
| Assess likelihood and impact | Scores with reasons |
| Respond | Controls or accepted risks with owners |
| Review | At least yearly, and after major change |
SOC 2 risk management readiness check
Tick what is already in place.
Your result appears here as you tick, so you can see what is still open.
Linking SOC 2 risk management to controls
Each significant risk should map to controls or a documented acceptance. As a result, the control set has a clear reason for existing.
- Risks without controls become gaps
- Controls without risks may be unnecessary
- Accepted risks need an owner and a date
- Changes trigger a fresh look
Oversight evidence
Leadership should see and approve the risk picture. So minutes or sign-offs from a management review are useful evidence. In addition, vendor and fraud risks belong in the same register.
The criteria are published as the AICPA Trust Services Criteria.
Which brand prepares it
Ridgeline Compliance builds risk processes as part of SOC 2 readiness. Also, Clearpoint Advisory explains how the examination treats them. Quantum Group Security is a holding company. So you describe the problem once, and we route you to the right brand. You then contract with that brand alone. That means one agreement, one fixed fee and one point of contact.
Also keep the register short. So it gets read and used.
SOC 2 risk management questions
Is SOC 2 risk management required?
Yes. Risk assessment is part of the criteria every SOC 2 report covers.
How often should SOC 2 risk management reviews happen?
At least yearly, and after significant change.
Who owns SOC 2 risk management?
Leadership, with a named person running the process.
Does the CPA firm write our risk assessment?
No. The organisation owns it, and the firm examines it.
Related guides
Start SOC 2 risk management in the right place
Tell us about your SOC 2 timeline. We route you to the right brand, usually within one business day.
Find the right brand